Authentication
Authentication controls how dashboard users sign in to Leena AI — the admins, agents, and builders who log in to configure and operate the platform. It also lets you limit sign-in to a defined set of networks, and this page explains how dashboard sessions end and how users are warned before they do.
This is separate from how employees authenticate into the assistant itself. Those settings live under Leena Channels (Apps authentication, Web authentication, Other auth settings, and SAML apps).

Where to find it
Open the Admin Console, then go to Dashboard settings → Authentication.
The page has two parts: choosing the sign-in method, and restricting which networks can reach the dashboard.
AvailabilityAuthentication is not available on trial licences. Where it is available, it opens for System Admin and for the Channel & Authentication Setup Manager role.
1. Select the type of authentication
Pick one of two methods. The choice applies to every dashboard user in the workspace.
Email + Password
Users sign in with their email address and a password. Selecting this reveals Configure Password Policy, where you set the rules new passwords must satisfy.
Character requirements — tick any combination:
- At least one uppercase letter
- At least one lowercase letter
- At least one number
- At least one symbol or non-numeric character, from
! @ # $ % ^ & ( ) * + = _ -
Maintain History — prevents people from cycling back to a recent password. Tick it, then set how many previous passwords to remember. Accepts a whole number from 1 to 9.
Set password expiry — forces a password change on a schedule. Tick it, then set the number of days a password stays valid. Accepts a whole number from 1 to 365.
Both numeric fields stay disabled until you tick the box above them, and both reject decimals and out-of-range values when you save.
Use Save to apply the policy, or Cancel to drop your edits and restore the last saved rules. Both stay inactive until you change something.
SSO
Users sign in through your identity provider using SAML. Selecting this reveals Single Sign On Set-up.
The fastest route is to upload the metadata file from your identity provider — an XML file up to 2 MB — which fills in the fields below for you. You can also enter them by hand:
| Field | What to enter |
|---|---|
| Name of the SSO provider | A label for the provider, shown to users on the sign-in screen |
| SAML URL | The sign-in URL your identity provider redirects users to |
| SAML issuer URL | The issuer identifier from your identity provider |
| Identifier Format | The name ID format, chosen from the list |
| Signature Algorithm | The signing algorithm, chosen from the list |
| SAML Certificate | The signing certificate issued by your identity provider |
Values to give your identity provider
The SAML Configuration block lower down holds the values your identity provider needs from Leena AI. These are generated for you and are read-only:
- Audience URL
- ACS URL
- Certificate
Use Download meta data file to hand these over as a single file rather than copying each value across.
Save your changes once the provider details are complete. Test the sign-in flow with a single account before rolling the change out, since it applies to everyone immediately.
2. Restrict IP Addresses
Limit dashboard sign-in to specific networks. Turn the toggle on, then add the ranges that should be permitted.
Each entry takes:
- Name of the IP address — a label so the entry is recognisable later, such as the office or VPN it belongs to
- The IP address and its CIDR value — the range, entered as the address followed by the network prefix
The page shows a running count of how many entries are in the list.
This list permits access rather than blocking itDespite the wording on screen, the entries you add are the ranges allowed to sign in. Once the toggle is on, anyone connecting from an address outside the list is refused — so an address you leave off is blocked, not the other way round.
Add every network your admins sign in from, including VPN egress ranges and any remote offices, and confirm your own address is covered before turning the toggle on. Enabling it with an incomplete list will lock you out of the dashboard.
3. Session expiry and re-authentication
Every dashboard session lasts a fixed time from sign-in. When it ends, the user is signed out and has to sign in again. Shortly before that happens, the dashboard warns them and lets them extend the session without losing their work.
Session length
Session length isn't set on this page. It's the Token expiry duration on Dashboard settings → Setup, entered in minutes. Left blank, sessions last 45 days.
If a user works across several workspaces, each workspace's own setting applies while they're in it.
The expiry warning
In the final 60 minutes of a session, an amber banner appears across the top of the dashboard:
Your session will expire in {time}. Re-authenticate now to stay signed in, or you will be logged out automatically.
The countdown updates every second and stays accurate even if the tab was in the background or the computer was asleep. For sessions of 60 minutes or less, the banner appears at the halfway point instead — a 30-minute session warns with 15 minutes left — so it isn't on screen from the moment the user signs in.
The banner shows for every dashboard user, whatever their sign-in method. With the default 45-day session, few users ever reach the warning window; it matters most where the token expiry duration has been shortened.
If a maintenance banner is also active, the session warning takes its place until the user deals with it.
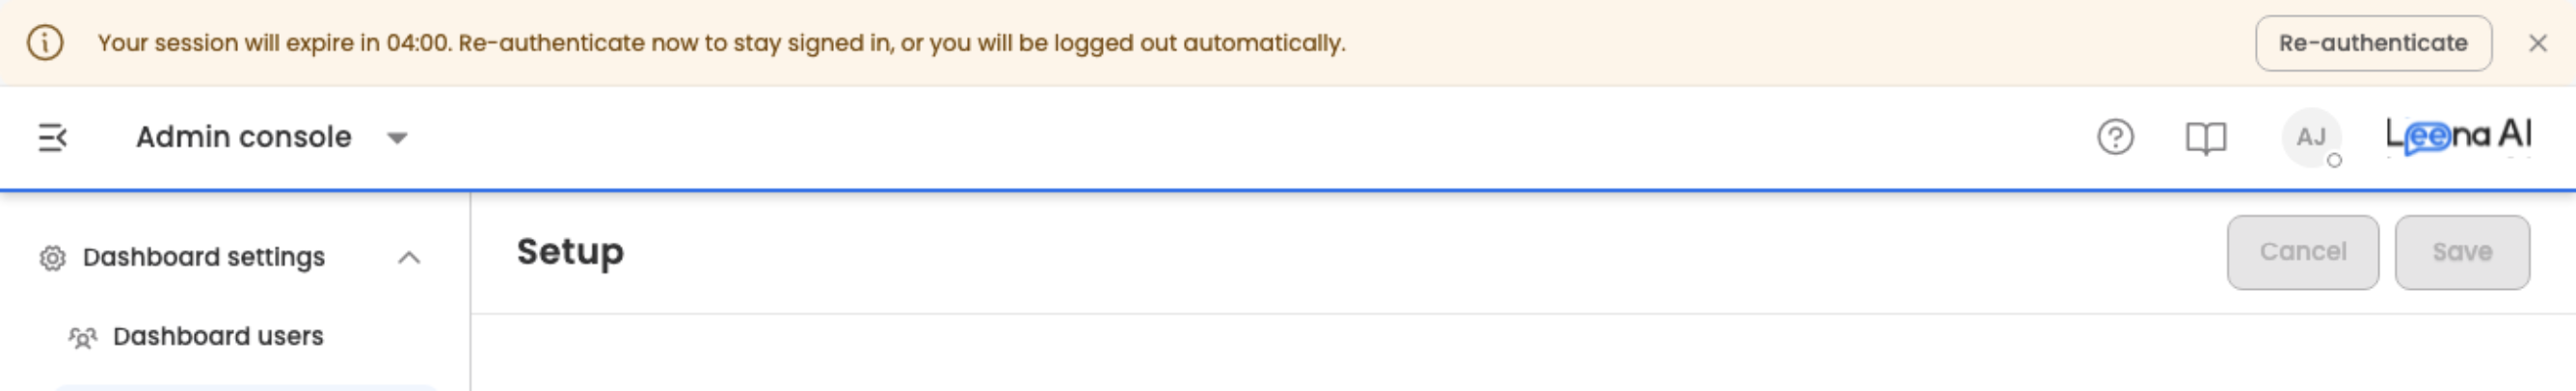
Re-authenticate
Re-authenticate opens the sign-in screen in a new tab, with a note explaining that this tab is only for extending the session. Once the user signs in there:
- The original tab picks up the new session on its own. It isn't reloaded or redirected, so open forms and unsaved work stay where they were.
- The sign-in tab closes itself. If the browser doesn't allow that, it shows Session extended instead, and the user can close it by hand.
If someone signs in as a different user in that tab, the original tab can't carry on silently. It shows Signed in as a different user, with Reload to continue as that account or Sign out. Unsaved changes on that screen are lost either way.
Dismissing the banner
The × hides the banner. It comes back in the final 5 minutes of the session so the logout is never a surprise, and can be dismissed again there.
When the session runs out
If the user doesn't re-authenticate, they're signed out automatically when the countdown reaches zero. The sign-in screen then explains why:
Your session expired, so you were signed out. Sign in again to pick up where you left off.
Updated 20 days ago